Technical safeguards for electronic protected health information
The HIPAA Security Rule asks you to control who can reach ePHI, record what they do with it, keep it from being altered, know who is on the other end and protect it on the wire. Ciyora runs those safeguards across your workforce, endpoints and cloud accounts and keeps the records an OCR investigator or auditor will ask for.
What the Security Rule asks
The HIPAA Security Rule (45 CFR Part 164, Subpart C) applies to covered entities (health plans, health care clearinghouses and most health care providers) and to their business associates. It requires administrative, physical and technical safeguards for electronic protected health information, based on a risk analysis of your own environment. The technical safeguards in 45 CFR 164.312 cover access control, audit controls, integrity, person or entity authentication and transmission security. Some implementation specifications are required and others are addressable, which means you implement them where reasonable and appropriate or document an equivalent measure.
Ciyora is a security platform, not an electronic health record. It helps with the technical safeguards and the administrative safeguards that depend on them, such as information system activity review, workforce clearance and termination, and security incident procedures.
Hosting location
Customer data is hosted in India. Self-hosted deployment is also available. Your business associate agreements and internal policies can include expectations about where ePHI and logs that may contain it are stored, so confirm the hosting arrangements meet your obligations before you adopt the hosted service, or run Ciyora Fabric self-hosted in your own environment.
How Ciyora maps to the requirement areas
Each row names a control area, what Ciyora does for it, and the evidence it can produce. Your own policies, people and processes still matter: the platform helps you operate and evidence the controls.
| Requirement area | How Ciyora helps | Evidence you can produce | Modules |
|---|---|---|---|
| 164.312(a)(1) Access control: unique user identification | One identity record per person across your identity provider, clinical and business applications and cloud accounts, matched from the HR source; orphaned and duplicate accounts detected. | Identity inventory with source system, and orphaned and duplicate account findings. | Fortress |
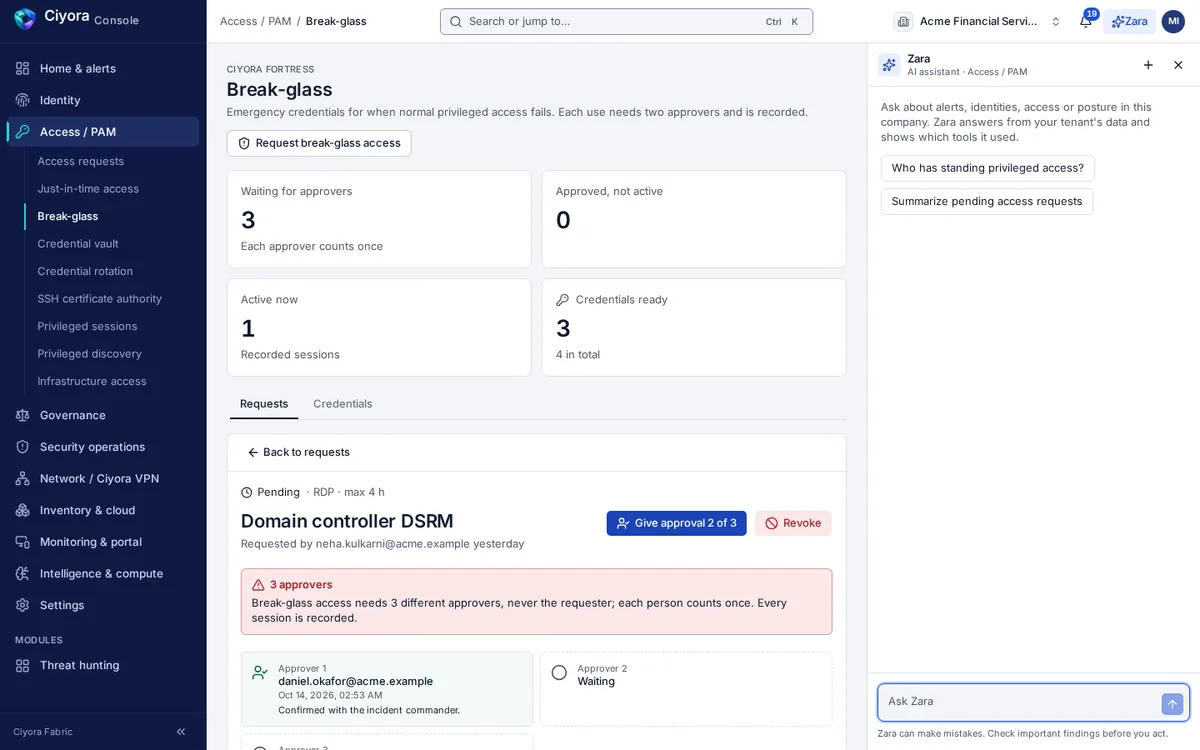
| 164.312(a)(1) Access control: emergency access procedure | Break-glass access that needs multiple approvers, never the requester, with every privileged session recorded. | Break-glass requests, approvals and session recordings. | Fortress |
| 164.312(a)(2)(iv) Encryption and decryption | Cloud posture checks for unencrypted storage, volumes and databases; device posture checks for disk encryption before network access is granted. | Posture findings mapped to the HIPAA control and their remediation; device posture results. | Armor, VPN |
| 164.312(b) Audit controls | Central log collection from systems that hold ePHI, with search and export; privileged sessions recorded; administrative actions in Ciyora written to a hash-chained audit log. | Log search and export, session recordings and audit chain verification. | Detect, Fortress, Comply |
| 164.312(c)(1) Integrity | File integrity monitoring on endpoints and servers through the Ciyora endpoint agent; detections for unauthorized changes and destructive activity. | File integrity events and related detections. | Detect |
| 164.312(d) Person or entity authentication | Single sign-on with your identity provider; MFA status per identity; just-in-time privilege that can require MFA to activate; security-key step-up to reveal a stored credential. | Identities without MFA, step-up records and privileged activation history. | Fortress |
| 164.312(e)(1) Transmission security | Remote access to clinical and back-office systems over the WireGuard mesh, deny by default, with no inbound ports; endpoint data-protection policies for file transfers and USB devices. | Versioned access policy, device posture results and data-protection events. | VPN, Monitor |
| 164.308(a)(1) Risk analysis and information system activity review | Asset and SaaS inventory with sensitivity and owners; vulnerabilities ranked by CVSS, EPSS and CISA KEV; risk register linked to controls; regular review of detections and access. | Asset inventory, vulnerability status over time and the risk register. | Discover, Comply, Detect |
| 164.308(a)(3) and (a)(4) Workforce security and information access management | Access requests with approval, periodic access reviews, and leaver deprovisioning driven by the HR system. | Access review evidence packs and joiner-mover-leaver reports. | Fortress, Comply |
| 164.308(a)(5)(ii)(C) Log-in monitoring | Baselines for authentication failures and unusual sign-ins, identity threat detection for credential attacks. | Authentication alerts and identity threat incidents. | Detect, Fortress |
| 164.308(a)(6) Security incident procedures | Incident queue with owner, severity and timeline of signals, notes and response actions; the record of when an incident was discovered supports breach assessment and notification decisions. | Incident records with discovery time, actions taken and closure notes. | Detect |
The clock starts at discovery
Under the HIPAA Breach Notification Rule, covered entities notify affected individuals without unreasonable delay and no later than 60 calendar days after a breach of unsecured protected health information is discovered (HHS, Breach Notification Rule). Ciyora Detect records when an incident was detected, who handled it and what was done, and Ciyora Fortress shows which identities and entitlements could reach the affected systems, so the facts you need for the risk assessment are in one place.
Please note. Ciyora is not a certification and does not make an organization compliant on its own. This page describes how Ciyora capabilities map to requirement areas and help you produce evidence. Always read the current text of the regulation or standard and take advice from your compliance team, auditors or legal counsel.
Walk through your control set with us
Bring your latest audit observations or gap assessment, and we will show where Ciyora fits and where it does not.