Know what you own and what is exposed
Ciyora Discover keeps one inventory of endpoints, servers, domains, certificates and cloud resources. It combines what the endpoint agent reports with network scans and cloud accounts, and ranks vulnerabilities by how likely they are to be exploited, not only by severity.
What Ciyora Discover does
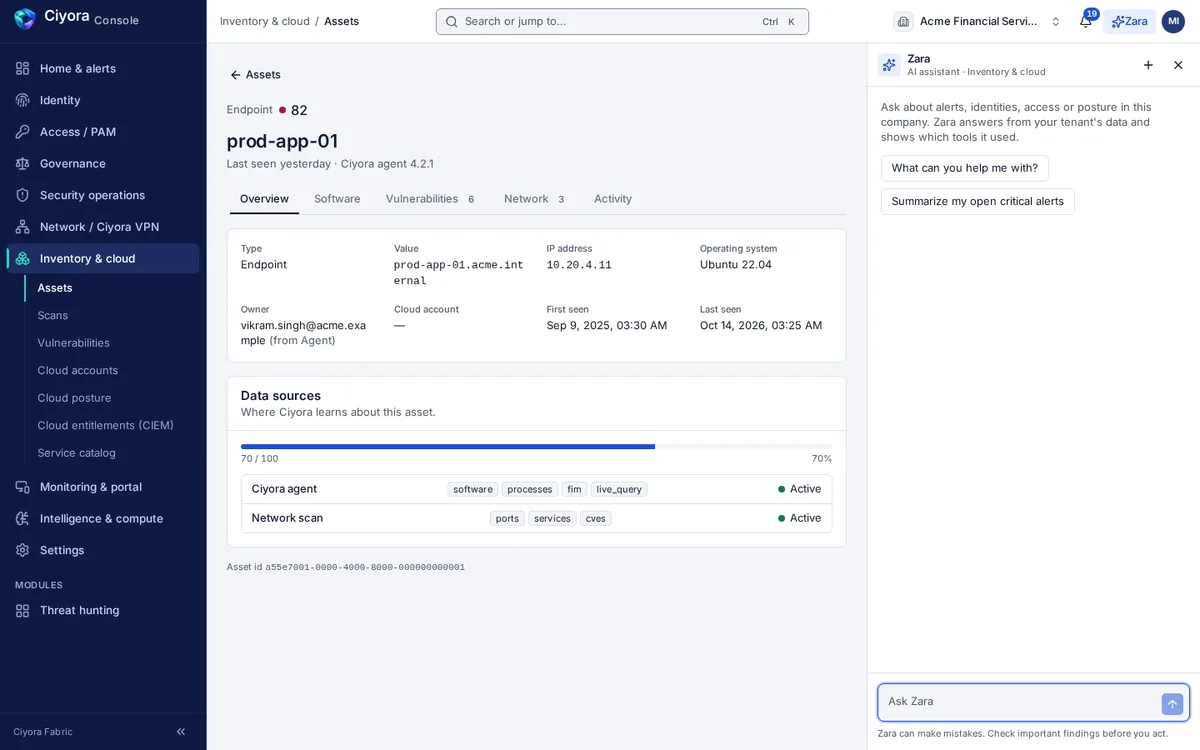
One asset, every source
Each asset shows where Ciyora learned about it and what each source contributes, so gaps in coverage are visible. Tabs cover installed software, vulnerabilities, network interfaces and open ports, and the activity related to the asset.
- Data sources per asset: the endpoint agent, network scans, cloud connectors and imported lists
- Asset import from CSV or spreadsheet files
- Inventory health that flags stale, orphaned and duplicate records
- Software inventory with versions and the CVEs that affect them
- Riskiest assets first, with owner and agent status
Vulnerabilities ranked by real-world risk
Findings combine CVSS with EPSS exploit-likelihood scores and a flag for entries on the CISA Known Exploited Vulnerabilities list. Filters for severity, status, exploitation and CVSS keep the work queue focused on what attackers use.
- CVE data kept current from the National Vulnerability Database
- Affected assets for each vulnerability
- Bulk status changes: mark fixed, accept the risk or mark a false positive with a reason, and reopen
Scans on your schedule
Run a scan against a registered target with a confirmation, follow its steps and failures, and cancel it if needed. The scan list refreshes on its own while scans run.
- Port scans, DNS enumeration, vulnerability scans and TLS configuration audits
- Credentialed scans for a deeper look at hosts you own
- Container image and package scans
- Scans run only against targets registered to your tenant
External attack surface
Discover finds internet-facing subdomains from certificate-transparency logs, fingerprints the technology behind them, probes ports and web services, and monitors certificates, so new exposure is noticed before it is exploited.
- Subdomain discovery, technology fingerprints and certificate monitoring
- Exposures that can be raised as tickets for the owning team
Code and supply chain
Scan a git repository or uploaded code for insecure patterns, vulnerable dependencies and committed secrets, and see which third-party components your software depends on.
- Static analysis (SAST), software composition analysis (SCA) and secrets scanning
- Supply-chain view of components and the vulnerabilities they carry
- Software bills of materials kept with each application and image
Service catalogue
SaaS applications and cloud services in one catalogue, with what each costs, how sensitive it is and who can use it. Unsanctioned applications and AI tools are called out.
- Risk, sensitivity, cost and licences in use for each SaaS application
- Who has access, through Ciyora Fortress
- Cloud services with provider, regions, approval and lifetime
Capabilities
- Asset inventory
- Endpoints, servers, domains, certificates and cloud resources with risk, owner, agent and data sources; CSV import and inventory health.
- Vulnerabilities
- CVSS with severity bands, EPSS, CISA KEV, NVD updates, status workflow with reasons and affected assets.
- Scans
- Port, DNS, vulnerability, TLS, credentialed, container image and package scans against registered targets, with steps, failures, open ports and cancellation.
- Attack surface
- Subdomain discovery from certificate-transparency logs, technology fingerprints, port and HTTP probing, certificate monitoring and exposure tickets.
- Code security
- SAST, SCA and secrets scanning for repositories and uploaded code, supply-chain view and SBOMs.
- Service catalogue
- SaaS applications and cloud services with risk, sensitivity, cost, licences in use, who has access, and callouts for unsanctioned and AI tools.
How Ciyora Discover works with the rest of the platform
Every module shares one tenant, one identity model, one audit chain and one console, so a finding in one place is context everywhere else.
Ciyora Discover can be bought on its own or as part of a bundle. See Ciyora Discover pricing.
See Ciyora Discover in a demo
A demo walks through the module on a sample tenant and covers how it would connect to your identity provider, cloud accounts and sites.