Govern every identity and every privileged session
Ciyora Fortress joins identity governance and privileged access management. It knows who and what holds access, routes every request through policy and separation-of-duties checks, grants privilege only for as long as it is needed, and records what happens with it.
What Ciyora Fortress does
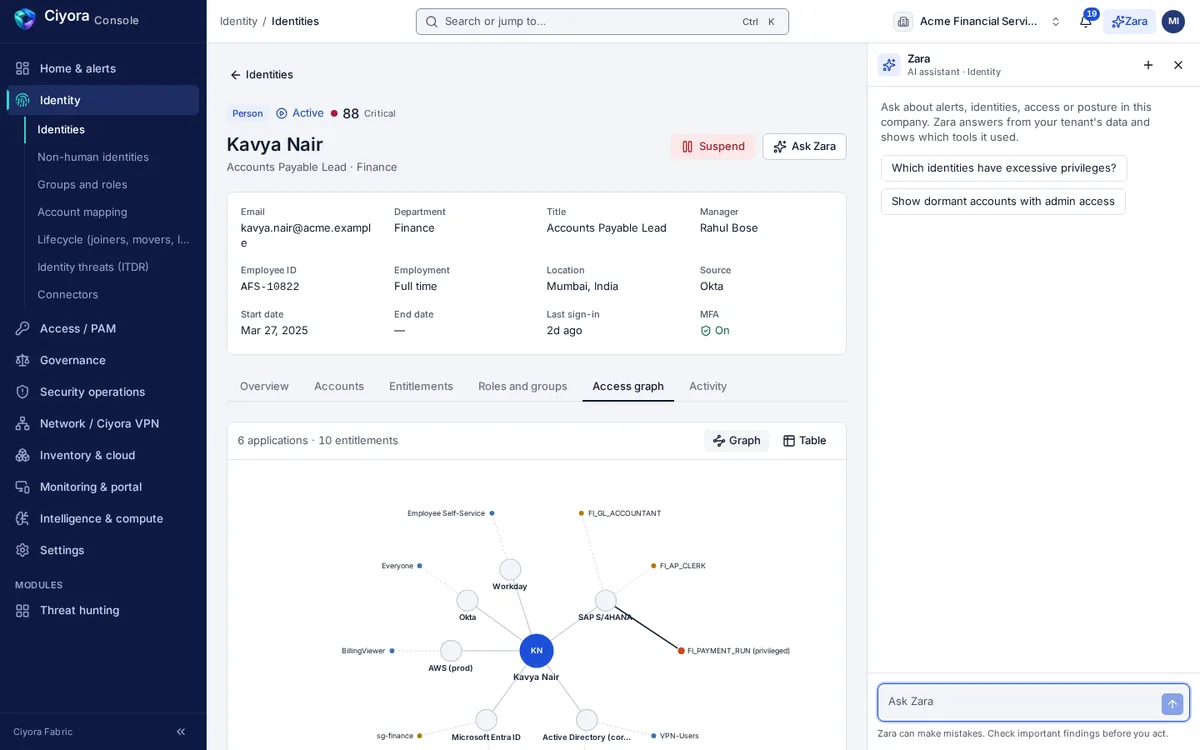
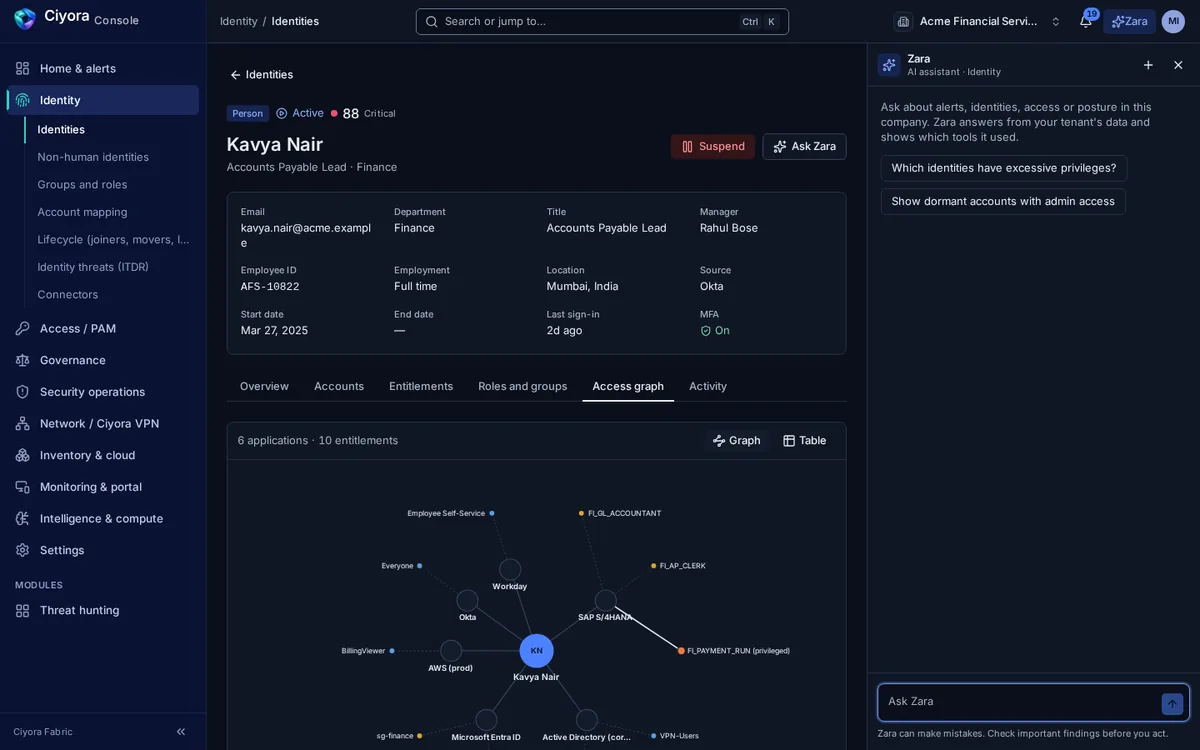
One identity record across every connected system
Fortress pulls people from your HR system and accounts from directories, identity providers, cloud providers and applications, then matches accounts to people. Orphaned and duplicate accounts are surfaced for an owner to link or disable, and each identity shows what it can reach.
- Identity detail with accounts, entitlements, roles and groups, activity, related assets and an access graph
- Blast radius per identity: the assets, grants and admin roles it would expose if compromised
- Risk score per identity, with filters for status, source and risk
- HR files in CSV or Excel imported with suggested column mapping, alongside live HR connectors
- Role mining that proposes roles from the entitlements people in a department share
Joiners, movers and leavers without the ticket chase
After each HR sync, Fortress detects who joined, moved or left and starts the matching lifecycle, with approval where you want it. Birthright rules grant day-one access, and access is added or removed directly where a connector can do it and through a service-desk ticket where it cannot.
- Birthright rules checked against the connectors you actually have
- Provisioning and deprovisioning in Active Directory and LDAP, Entra ID, Okta, AWS IAM, Kubernetes and PostgreSQL
- Tickets opened in your service desk, such as ServiceNow or Jira, for systems without a direct connector, with drift reconciled afterwards
- Leaver mailbox and drive ownership handed to a named person
- Inbound SCIM 2.0 for applications that push their users to Fortress
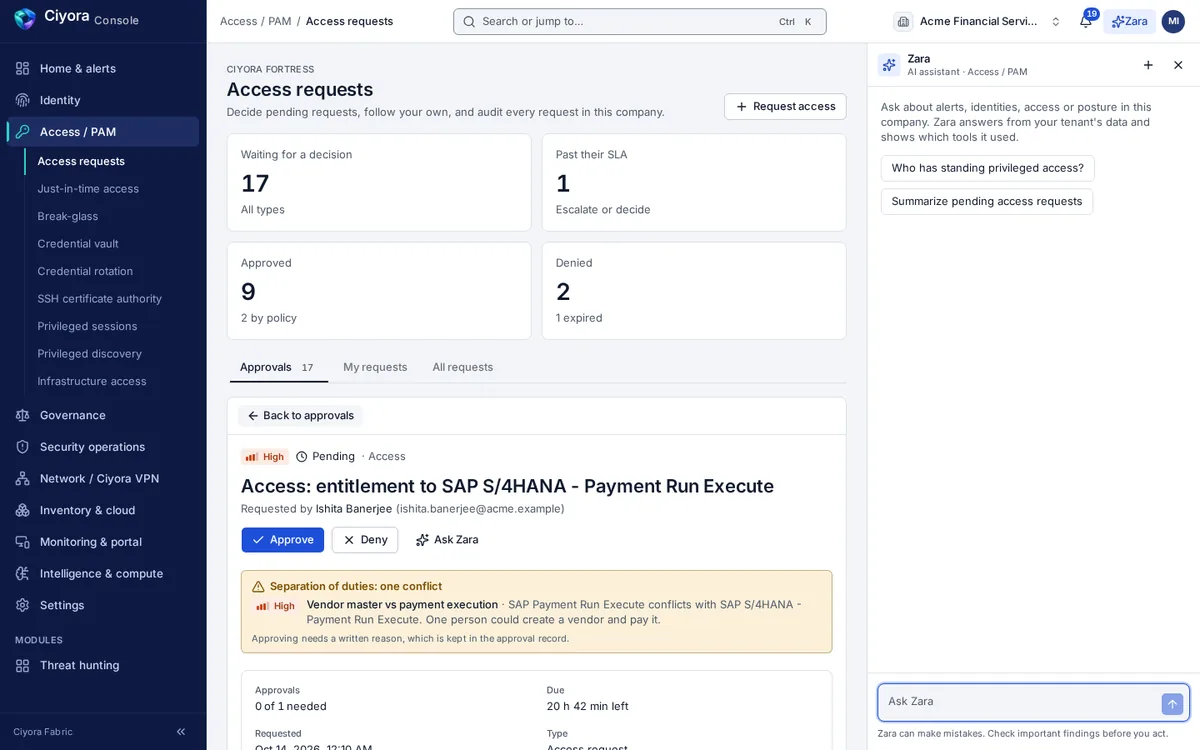
Access requests with separation of duties built in
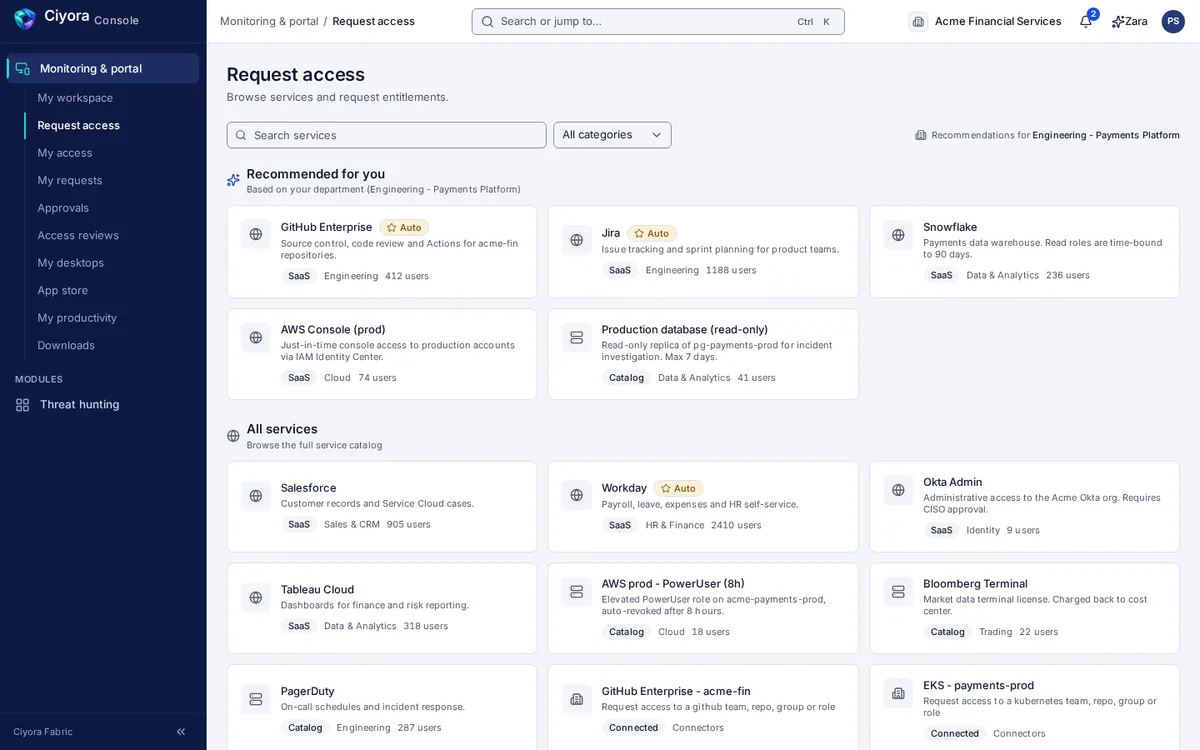
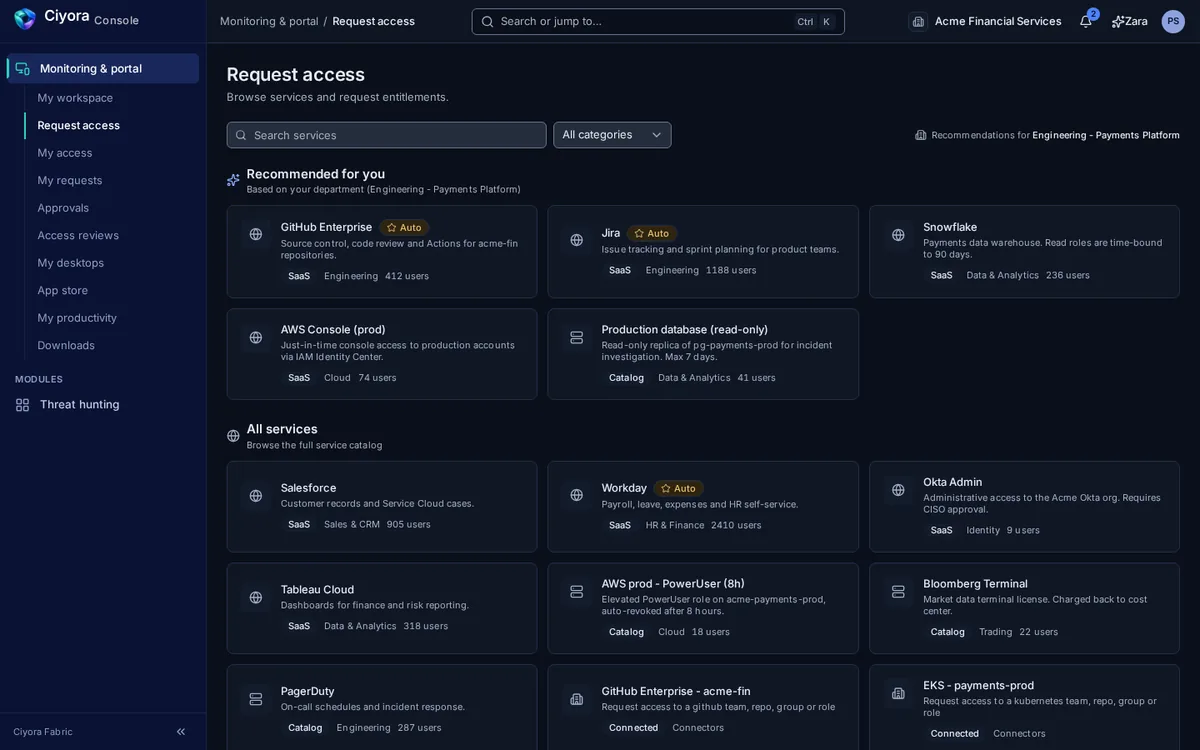
People request access from a self-service catalogue with recommendations for their department and bundles for common roles. Approvers see the request with its separation-of-duties result, and a conflicting request needs a written reason that is kept with the decision.
- Catalogue of SaaS, cloud and connected applications, with levels, durations and Kubernetes namespace scoping
- Approval centre for access, just-in-time and break-glass requests, with SLA warnings and bulk decisions
- Time-bound delegation of approvals while an approver is away
- Approve from the Ciyora mobile app, with the same rules as the console
- Every decision, reason and approver written to the hash-chained audit log
Separation of duties you can test before you change
SoD policies cover conflicts inside one application and across applications. Fortress checks them before a request is approved, scans existing access for violations, and records exceptions with an owner and an end date.
- Preventive check at request time and scheduled detective scans
- Simulation that runs proposed role changes through the same check before you make them
- Time-bound exceptions that move the violation out of the open queue in the same step
Access reviews that finish on time
Review campaigns are built from current access, ordered by risk and decided in bulk where it is safe. High-risk privileged identities get targeted micro-certifications as soon as they appear, instead of waiting for the next quarter.
- Manager, application and privileged-access campaigns, one-off or recurring on a schedule
- Risk-ordered work queues, with a written reason to revoke or to certify high-risk items
- Zara suggests certify or revoke with a confidence score; the reviewer decides
- Review from the console or the Ciyora mobile app
- Evidence packs exported as CSV or JSON, with a content hash on the JSON pack
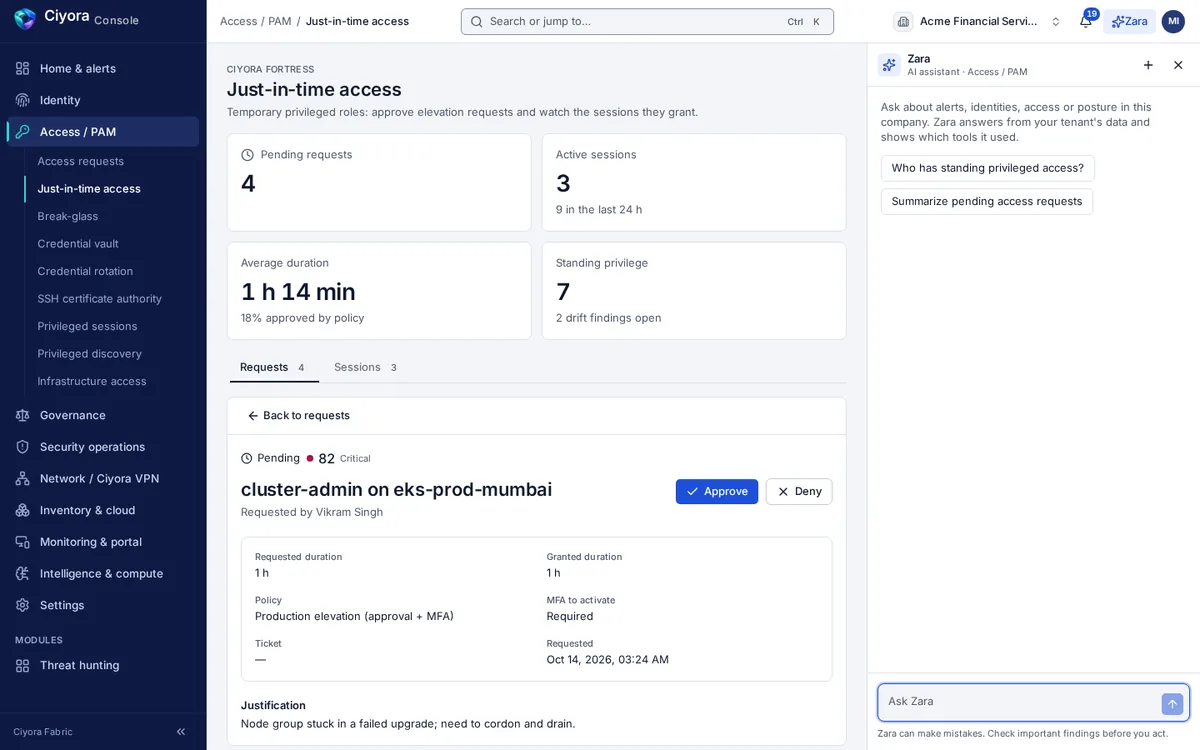
Just-in-time privilege instead of standing admin rights
Privileged roles are requested for a set duration against a policy that can require approval and MFA to activate. Sessions are visible while they run and can be extended or revoked with a reason.
- Elevation for cloud consoles, Kubernetes clusters, databases and servers
- Endpoint privilege management: policies for admin elevation on laptops and servers, with approval when needed
- Standing-privilege and drift findings for accounts that keep access they no longer use
- Approve, deny, extend and revoke from the console, the approval centre or the mobile app
Break-glass with dual control
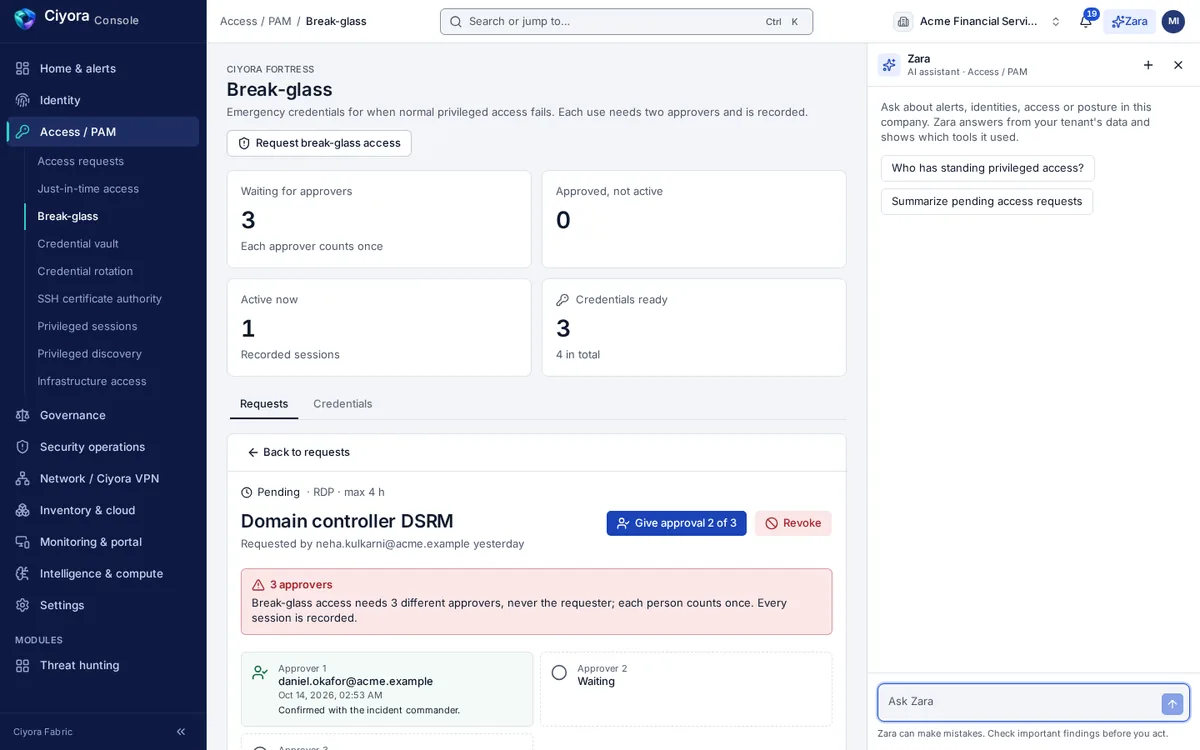
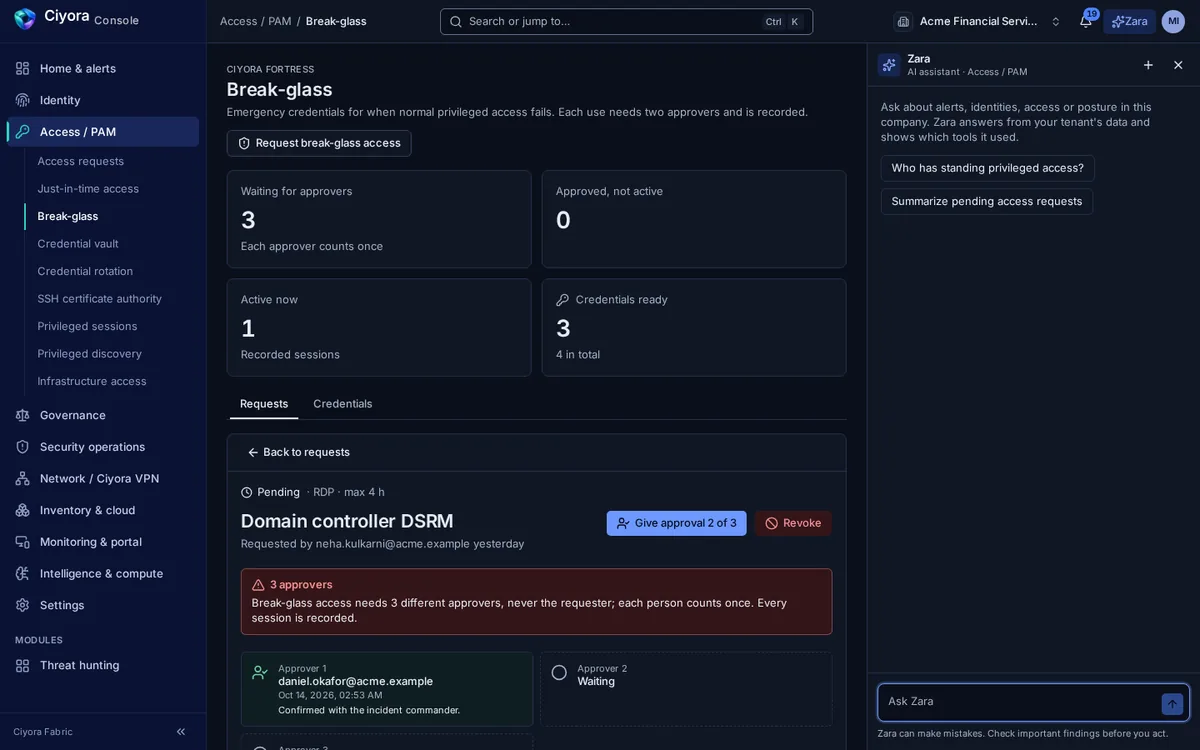
Emergency credentials are released only after the required number of different approvers agree. The requester can never approve their own request, each approver counts once, and every session is recorded.
- N-of-M approval from named keyholders, from the console or the mobile app
- Only the requester can activate, and revoking needs a reason
A credential vault that keeps secrets out of sight
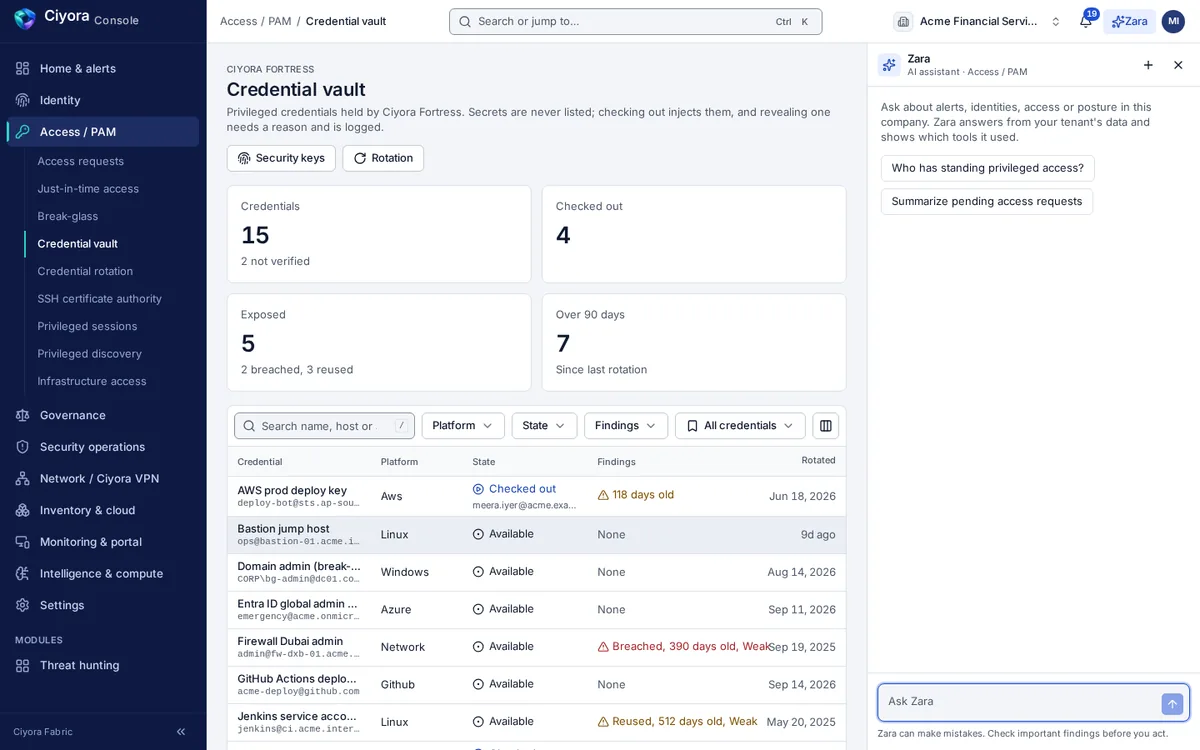
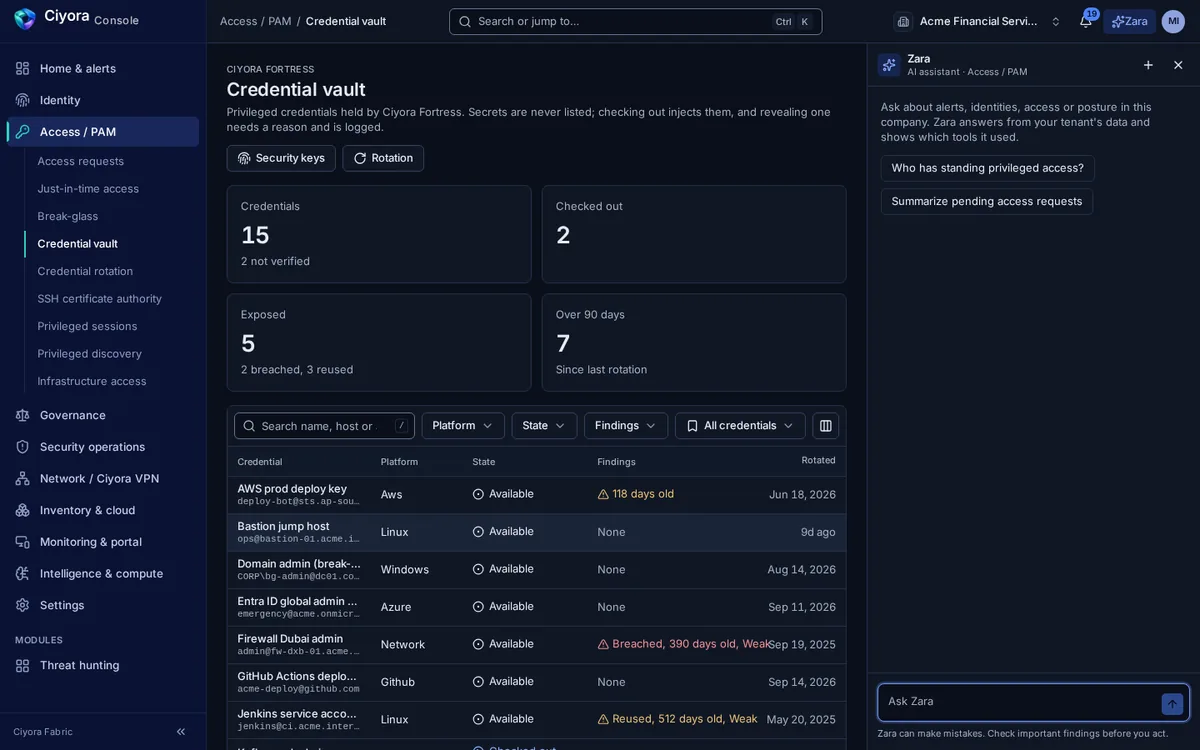
Privileged credentials are held encrypted in the vault. Checking one out injects it into the session; revealing it needs a reason and a step-up with a security key or passkey. Rotation runs on schedule and verifies the new secret before it is trusted.
- Findings for breached, reused, weak and overdue credentials
- Rotation for SSH, Windows, Active Directory, Entra ID app secrets, AWS IAM, Google Cloud service account keys, Kubernetes service account tokens and common databases
- SSH certificate authority with short-lived certificates, key rotation, revocation and trust deployment
- Privileged account discovery that scans your systems and onboards what it finds into the vault
Privileged sessions and infrastructure access
People reach servers, databases, clusters and cloud consoles through Fortress instead of holding long-lived credentials. Each session uses short-lived access created for it and is recorded.
- SSH and RDP in the browser from Ciyora Console, without a jump box
- Databases through a temporary database role created for the session
- Kubernetes through short-lived RBAC and a kubeconfig that expires
- AWS, Azure and Google Cloud consoles through short-lived federated credentials
- Windows servers through temporary local accounts, and mainframes over TN3270 and 5250
- SSH recordings with replay and command search, RDP and VNC recordings, and a live view of running sessions with warn and terminate
Non-human identities with an owner and an expiry
Service accounts, API keys, tokens, certificates and workload identities are discovered from your connectors and given an owner, a rotation policy and an expiry. AI agents and MCP servers are registered as identities too, so they are reviewed like everything else.
- Inventory with owner, last use, rotation and expiry hygiene, and risk
- Rotation through the vault and overdue-rotation findings
- Certification campaigns for non-human identities
- Registries for AI agents, MCP servers and workload identities
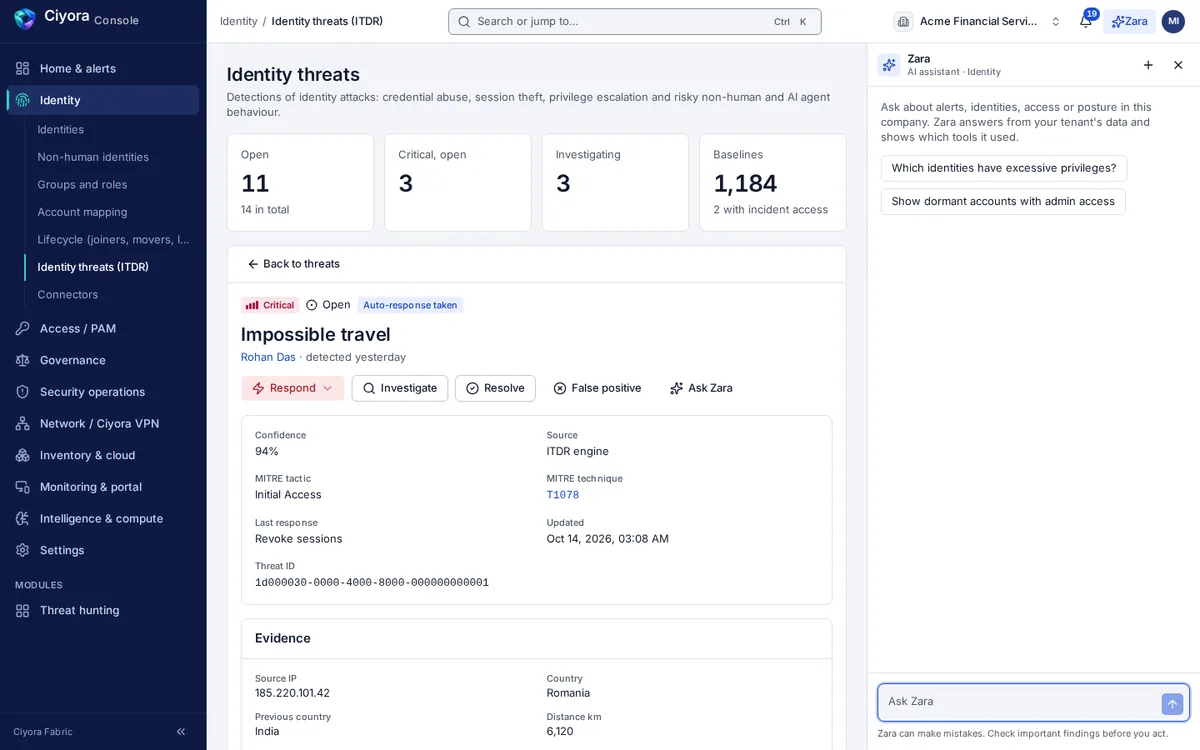
Identity threat detection and response
Fortress watches sign-in and access behaviour for signs of credential abuse, session theft and privilege escalation, and maps each detection to MITRE ATT&CK. Continuous access evaluation keeps a trust score for each identity that falls as threats open, with every deduction explained.
- Detections from identity-provider sign-in events and behavioural baselines
- A “No, it’s not me” answer in Ciyora Verify raises a suspected-compromise signal
- Analysts track each threat, suspend the identity when needed and record the response, all in the audit log
Contractors, vendors and guests
People who are not on your payroll get an identity with a sponsor who is. Contractor and vendor access is granted for a set period and reviewed like employee access.
- Sponsored identities with a named sponsor
- Time-bound contractor and vendor access
Everything in Ciyora Fortress
- Identity governance (IGA)
- Identities, accounts and entitlements from connected systems; account matching, orphan and duplicate detection; roles, groups and role mining; access graph, blast radius and risk scores.
- Lifecycle and provisioning
- Joiner, mover and leaver detection, birthright rules, provisioning to directories, identity providers, AWS IAM, Kubernetes and databases, service-desk tickets for the rest, and inbound SCIM 2.0.
- Access requests
- Self-service catalogue with recommendations and bundles, approval centre, bulk decisions, delegation and approvals on the mobile app.
- Access reviews
- Manager, application, privileged and non-human identity campaigns, recurring schedules, micro-certifications for high-risk identities, Zara suggestions and evidence export as CSV or JSON.
- Separation of duties
- Policies within and across applications, preventive checks at request time, scheduled scans, simulation of proposed changes and recorded exceptions.
- Privileged access (PAM)
- Just-in-time elevation, break-glass dual control, credential vault with step-up reveal, automated rotation, SSH certificate authority, privileged account discovery and endpoint privilege management.
- Privileged sessions
- Browser SSH and RDP, database, Kubernetes, cloud console, Windows and mainframe access with short-lived credentials; recordings with replay and command search; live view with warn and terminate.
- Non-human identities
- Service accounts, API tokens, keys, certificates, workload identities, AI agents and MCP servers with owner, rotation and expiry hygiene, risk and review.
- Identity threats (ITDR)
- Detections from sign-in events and behavioural baselines, mapped to MITRE ATT&CK, with continuous access evaluation and an audit trail of every response.
- Connectors
- Directories and identity providers, HR systems, service desks, cloud providers, SaaS applications, databases, PAM tools and mainframe security (RACF, ACF2, Top Secret), plus generic SCIM, REST and CSV.
- Audit and reports
- Hash-chained audit log that you can verify in the browser, access certification evidence packs and governance reports.
How Ciyora Fortress works with the rest of the platform
Every module shares one tenant, one identity model, one audit chain and one console, so a finding in one place is context everywhere else.
Ciyora Fortress can be bought on its own or as part of a bundle. It is also available in the Ciyora Zero Trust bundle with Ciyora VPN. See Ciyora Fortress pricing.
See Ciyora Fortress in a demo
A demo walks through the module on a sample tenant and covers how it would connect to your identity provider, cloud accounts and sites.