Private network access that follows identity, not location
Ciyora VPN connects laptops, servers and site gateways in an encrypted WireGuard mesh. Policy decides which people, groups and tagged devices can reach which hosts and ports. Anything not allowed is denied, and no inbound firewall ports are needed.
What Ciyora VPN does
A mesh, not a hub
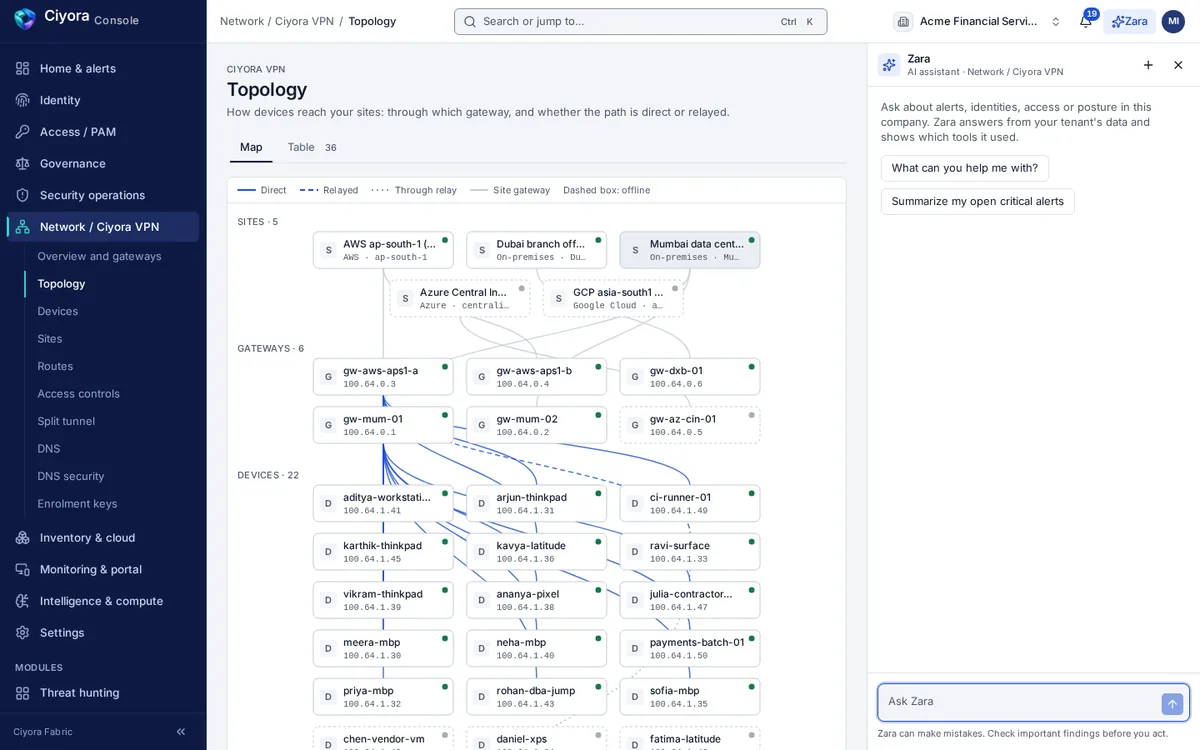
Devices connect directly to each other and to gateways whenever the network allows, using NAT traversal. When a direct path is not possible, traffic falls back to an encrypted relay. The control plane distributes keys and policy; it does not sit in the data path.
- WireGuard tunnels with direct UDP paths and relay fallback
- Mesh health, gateway heartbeats, relay health and load, and per-device path and latency in the console
- Clients keep their last network map if the control plane is briefly unreachable
- Every device gets a stable internal name on the mesh
Site gateways that dial out
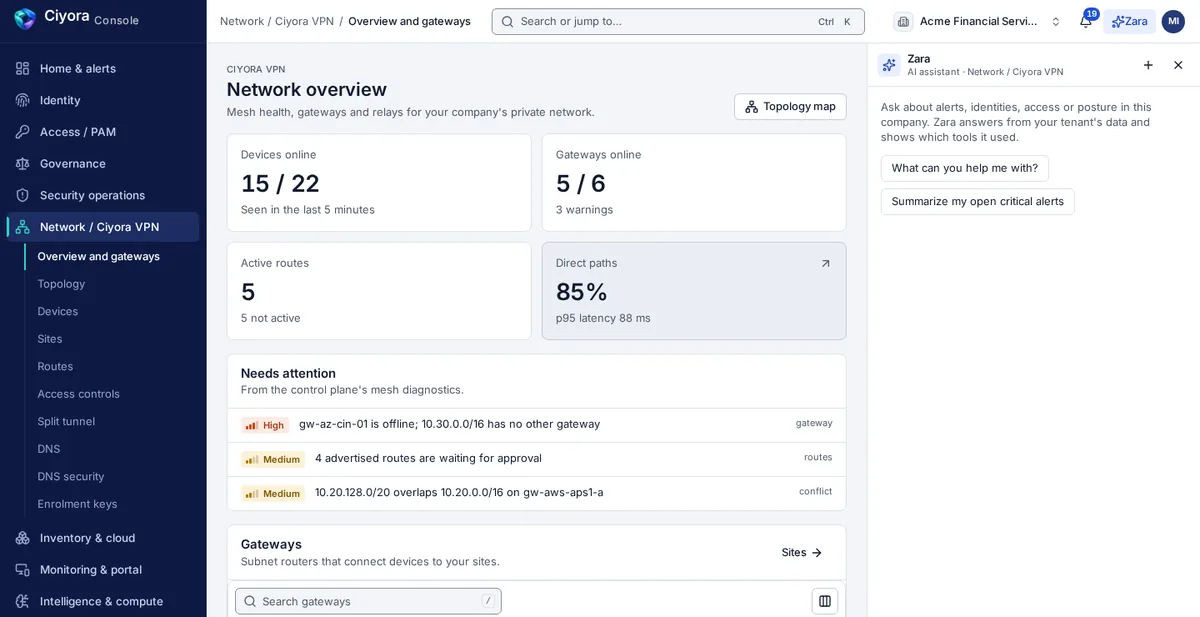
A gateway in each office, data centre or cloud network advertises its subnets into the mesh. It registers outbound to Ciyora Fabric and learns its peers from there, so you do not open inbound ports or publish a VPN concentrator to the internet.
- Advertised routes wait for approval before they carry traffic
- Overlapping routes and offline gateways are flagged
- Primary and failover gateways per site for high availability
- Exit nodes for people who need all their traffic to leave through a company network
Policy you can review like code
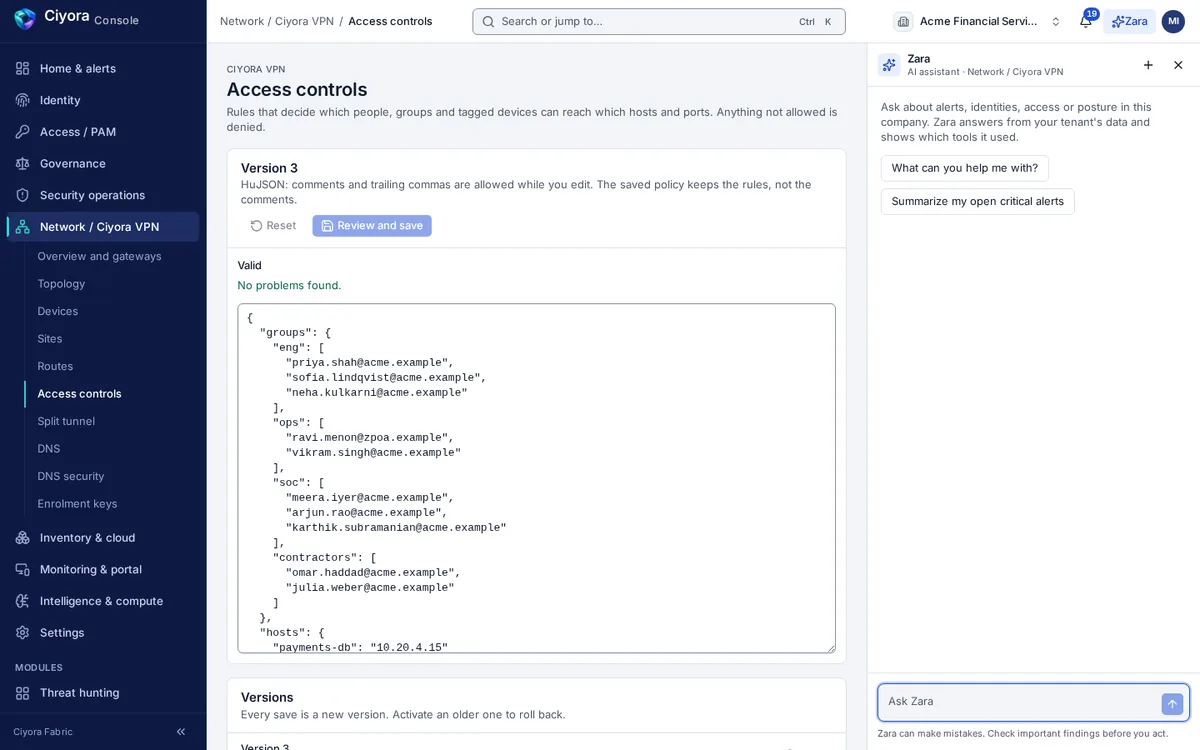
Access controls are written as a readable policy of groups, hosts, tags and ports. The editor validates as you type, shows a diff against the active version before saving, and keeps every version so you can go back to an earlier one.
- Deny by default: anything the policy does not allow is refused
- Test a policy against a sample connection before you save it
Just-in-time network access
Some paths should exist only while someone needs them. People request access to a network path, an administrator approves or denies it, and the grant is added to the network map for its duration and removed when it ends or is revoked.
Devices you can trust
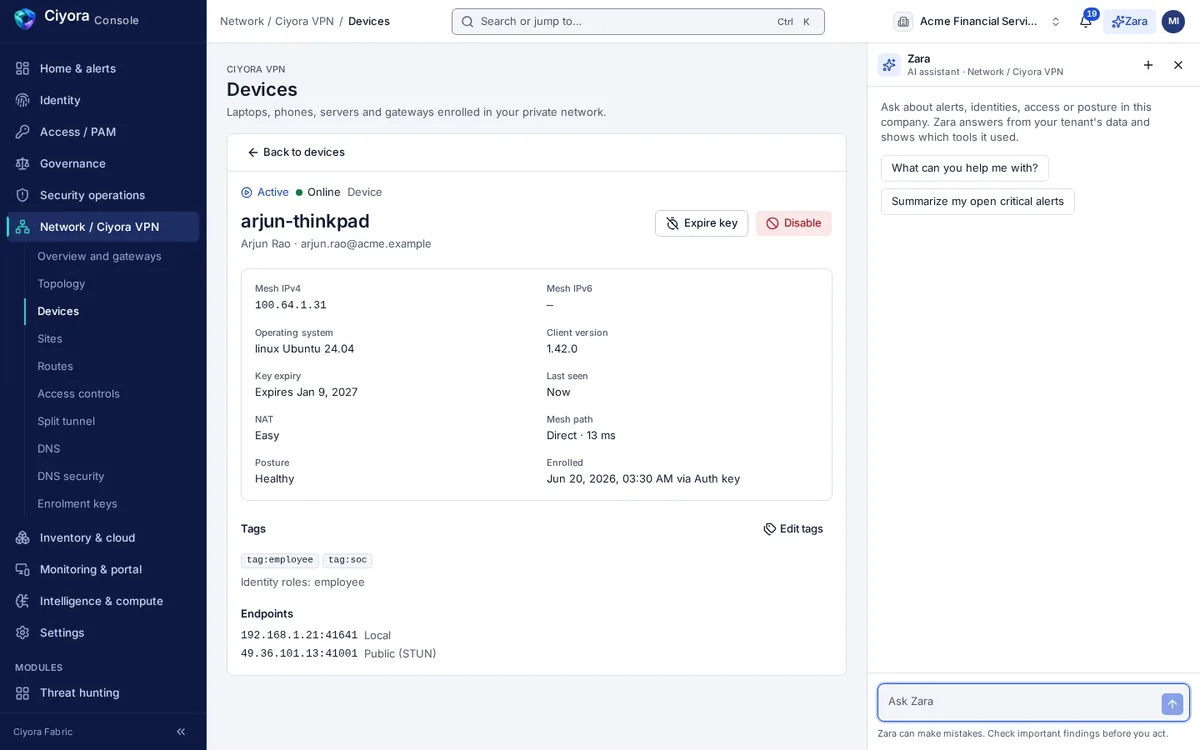
Every device enrols with a key that can expire, be single-use or be limited to tags. Ciyora Client reports posture such as OS version, disk encryption, firewall and screen lock, and devices can be disabled or have their keys expired from the console.
- Separate keys for user devices, MDM roll-outs and gateways; reusable or ephemeral
- Managed installers and connection profiles for Microsoft Intune and Jamf
- Posture checks for OS version, disk encryption, antivirus, screen lock, OS updates, firewall and client version
DNS that keeps internal names internal
Internal domains resolve through the tunnel with split DNS, private records live in the console, and DNS security blocks known-malicious domains before a connection is made.
- Split DNS with your own resolvers and private DNS records
- DNS security policies, blocked-domain reporting and a query log
- Indicators of compromise synced to clients
Hardening for sensitive networks
For networks that must stay dark, single packet authorization means the control plane answers only clients that knock first. On Linux, an identity-aware packet filter enforces policy in the kernel, and on macOS and Linux a kill switch blocks traffic outside the tunnel.
On every device, including phones
Ciyora Client runs on Windows, macOS and Linux, and the Ciyora mobile app brings the same mesh to iOS and Android, with exit nodes and the company networks the policy allows. Connect, disconnect and authentication events are sent to Ciyora Detect.
Capabilities
- Access controls
- Deny-by-default policy by user, group, device tag, host and port, with validation, diff, test, version history and roll back.
- Just-in-time access
- Requests for network paths, approved, denied or revoked by an administrator and applied to the network map for their duration.
- Sites and routes
- Site gateways advertise subnets; routes are approved, disabled or managed; primary and failover gateways; exit nodes; overlaps and offline gateways are reported.
- Split tunnel
- Per role or person: which networks go through the tunnel, which networks and domains stay off it, and whether that is enforced.
- DNS
- Split DNS for internal domains, private DNS records, internal device names, and DNS security that blocks known-malicious domains with a query log.
- Enrolment keys
- Expiring, reusable or single-use, ephemeral and tagged keys for devices, MDM and gateways. The full key is shown once and never stored by the console.
- Device posture
- OS version, disk encryption, antivirus, screen lock, OS updates, firewall and client version, evaluated per device.
- Topology
- A map of sites, gateways, devices and relays with direct and relayed paths, also available as an accessible table.
- Hardening
- Kill switch on macOS and Linux clients, single packet authorization for dark-network mode, and an identity-aware packet filter on Linux.
- Clients
- Ciyora Client for Windows, macOS and Linux, and the Ciyora mobile app for iOS and Android.
How Ciyora VPN works with the rest of the platform
Every module shares one tenant, one identity model, one audit chain and one console, so a finding in one place is context everywhere else.
Ciyora VPN can be bought on its own or as part of a bundle. It is also available in the Ciyora Zero Trust bundle with Ciyora Fortress. See Ciyora VPN pricing.
See Ciyora VPN in a demo
A demo walks through the module on a sample tenant and covers how it would connect to your identity provider, cloud accounts and sites.